

Smart Home Privacy Risks Explained: UK Guide 2026
Table of Contents
- What Smart Home Privacy Risks Actually Look Like in Practice
- Smart Home Data Collection Policies: What Companies Actually Do With Your Data
- How to Secure Smart Home Devices: A Practical Checklist
- IoT Security Standards UK: What Protects You and What Doesn't
- Local Control: The Privacy Advantage Most People Overlook
- Smart Home Privacy Risks Explained: Common Myths That Need Debunking
- Frequently Asked Questions
Last Updated: September 17, 2026
What Smart Home Privacy Risks Actually Look Like in Practice
Smart home privacy risks are the ways connected devices collect, transmit, and expose information about your household, often without you noticing. At DigIoT, we see buyers focus on hacking headlines while the quieter problem, routine data collection, goes unexamined. A smart speaker that wakes on a stray word, a camera that streams to a server you've never heard of, a door sensor that logs every time you leave: each one produces a record of your daily life.
That record is the actual product for many vendors. The device is simply the collection point.
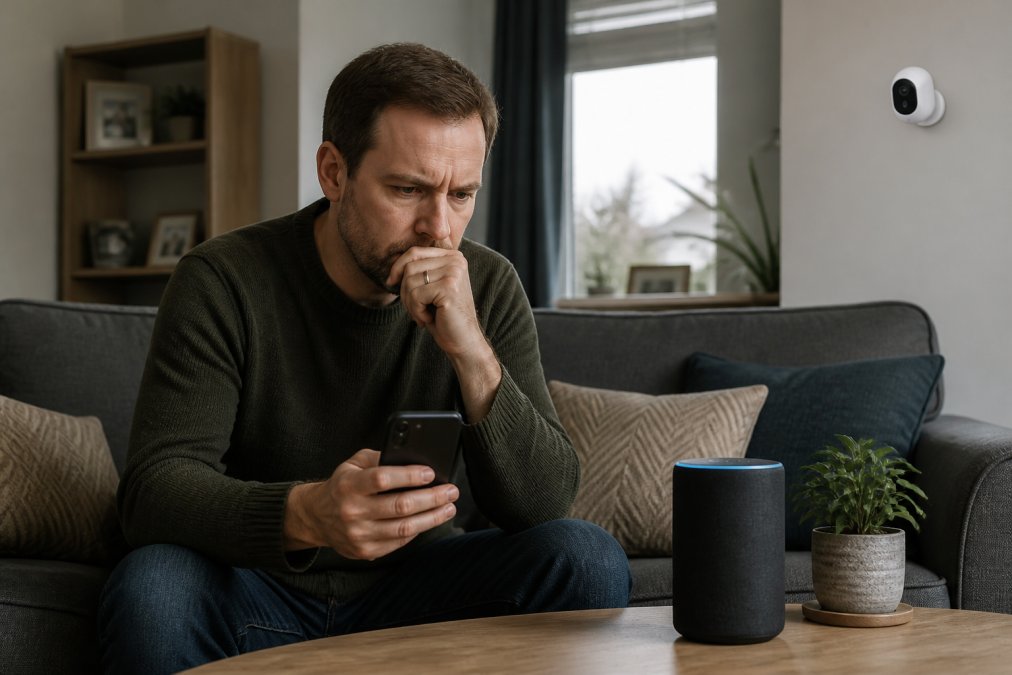
Always-on microphones and cameras
Devices with microphones or cameras hold the most sensitive position in your home. They sit in bedrooms, hallways and living rooms, listening and watching continuously so they can respond instantly.
The risk is not that someone is listening right now. It's that the device has the capability, the connection, and often the contractual permission to capture audio or video and process it elsewhere.
Metadata: the data you never see
Metadata is the information about your activity rather than its content: timestamps, frequency, device names, room locations, and patterns of use. A motion sensor doesn't record your face, but it records that the hallway was active at 2:14am every night for a fortnight.
That pattern is more revealing than a single image. It tells a story about shift work, illness, holidays, or an empty house.
Smart Home Data Collection Policies: What Companies Actually Do With Your Data
Most manufacturers collect more than the minimum needed to run a device. Typical categories include device identifiers, usage logs, network information, and in some cases audio or video snippets for "quality improvement."
Where the data goes varies. Some vendors process locally and delete quickly. Others retain records indefinitely, share with advertising partners, or transfer data internationally.
The practical question is never "do they collect data?" Almost all do. It's "what do they keep, for how long, and who else sees it?"
Reading a privacy policy without falling asleep
Go straight to four sections: what data is collected, how long it's retained, who it's shared with, and how to delete it. If retention is described as "as long as necessary" with no limit, treat that as indefinite.
How to Secure Smart Home Devices: A Practical Checklist
Securing a smart home comes down to reducing what each device can send out and tightening who can reach it. Work through this before adding anything new.
- Change every default username and password before the device goes live
- Enable two-factor authentication on the manufacturer account
- Put smart devices on a separate Wi-Fi network or guest SSID
- Disable remote access features you don't actively use
- Turn off audio or video recording where the device allows it
- Check for firmware updates monthly, not once at setup
- Review app permissions and revoke anything unrelated to function
- Delete old device data from vendor accounts when you stop using a product
The single most effective step is network separation. A compromised smart plug on its own network can't reach your laptop.
What most guides miss is that firmware updates matter more than passwords. A strong password on an unpatched device still leaves known vulnerabilities open.
IoT Security Standards UK: What Protects You and What Doesn't
IoT security standards in the UK centre on the Product Security and Telecommunications Infrastructure Act and the code of practice that shaped it. These set baseline requirements for consumer connectable products sold here, including bans on universal default passwords.
The Product Security and Telecommunications Infrastructure Act 2022 places duties on manufacturers, importers and distributors. It requires that consumers can report security issues and that default passwords are unique or changed at first use.
What it does not do is certify that a device is private. A product can meet the legal baseline and still send generous telemetry to its maker.
Local Control: The Privacy Advantage Most People Overlook
Local control means the device's core functions run on your own network rather than depending on a manufacturer's cloud. Commands, automations and recordings stay inside the home.
The privacy benefit is straightforward: data that never leaves your network can't be retained, sold, or exposed in someone else's breach. It also means the device keeps working if the vendor's servers go offline.
Devices that support local processing include the Aqara Presence Sensor FP2, which detects presence using millimetre-wave radar rather than a camera. It tracks up to five people across 30 zones without capturing any image at all. For video, the Aqara Camera E1 supports HomeKit Secure Video with encrypted storage, and local microSD recording up to 512GB. The Shelly BLU Door/Window Sensor reports open and closed states over Bluetooth Low Energy with no cloud account required.


| Device | Data approach | Local storage | Cloud required |
|---|---|---|---|
| Aqara Presence Sensor FP2 | Radar, no image capture | On-network processing | No |
| Aqara Camera E1 | Encrypted video | microSD up to 512GB | Optional |
| Shelly BLU Door/Window Sensor | Open/closed state only | None needed | No |
Smart Home Privacy Risks Explained: Common Myths That Need Debunking
The most persistent myth is that smart home privacy risks only matter if you have something to hide. In reality, the value of household data is in its patterns, not its secrets. Knowing when a home is empty is useful to a burglar and to an advertiser.
Another common belief is that covering a camera makes you private. It addresses one device while the microphone, motion sensor and hub carry on reporting.
A third myth says local control is only for technical users. Standards-driven devices have made it a setup choice rather than a project. Which? smart home security guidance consistently recommends checking data practices before purchase, not after.
Frequently Asked Questions
What are the main privacy risks associated with smart home devices?
The biggest risks are continuous audio and video capture, metadata logging (when you're home, which rooms you use, your daily routines), and data being shared with third parties or used for profiling. Many devices send data to cloud servers by default, and some privacy policies allow sharing with advertising partners. Weak default passwords and unpatched firmware also create entry points for attackers. Choosing devices with local storage and local control, such as the Aqara Camera E1, reduces how much data leaves your home.
How does the UK GDPR protect smart home users?
UK GDPR gives you the right to access, correct, and delete personal data that companies hold about you, including data collected by smart home devices. Companies must have a lawful basis for processing your data and must be transparent about what they collect. If a smart home company breaches these rules, you can complain to the Information Commissioner's Office (ICO). The ICO has the power to fine companies up to 4% of annual global turnover or £17.5 million, whichever is higher.
How can I secure smart home devices without cloud dependency?
Start by choosing devices that support local control and local storage. The Aqara Camera E1, for example, supports HomeKit Secure Video and local microSD storage up to 512GB, so footage doesn't have to leave your home. Change default passwords, enable two-factor authentication where available, keep firmware updated, and segment your smart devices onto a separate Wi-Fi network. Devices using Matter or Zigbee often process commands locally rather than routing everything through a cloud server.
Are smart home devices required to comply with UK data protection laws?
Yes. Any company processing personal data from UK residents must comply with UK GDPR, regardless of where the company is based. This includes smart home manufacturers, app providers, and cloud storage services. The Product Security and Telecommunications Infrastructure (PSTI) Act 2022 also requires consumer smart devices sold in the UK to meet minimum security standards, such as banning universal default passwords. If you believe a company is mishandling your data, you can report it to the ICO.
Smart home privacy is manageable, but only if you treat data collection as a design choice rather than an unavoidable cost of convenience. DigIoT curates standards-driven devices that work over Matter, Zigbee and Wi-Fi, with no vendor lock-ins and no forced subscriptions, so your automations stay under your control. Our plain-English advice and ongoing support help you build a setup that keeps working even if a manufacturer changes direction. Get started with DigIoT and show me the goods.